

Security & Access
Developer friendly

A token for one job can't touch the rest
An automation that writes evidence never gets the keys to your whole account. Both organization tokens and personal access tokens are scoped by object and action, so each one can do exactly its job and nothing more.
- Scoped to read, write, or delete on the objects you choose
- Revoke a single token without breaking the integrations next to it
PERMISSIONS FLOW DOWNPlatform groupGRANTEDEvery member of itINHERITEDObjects attached to itINHERITEDAPI TOKENS FOLLOW THE SAME MODELAn integration tokenORG SCOPEDSCOPED TOA SPECIFIC OBJECT TYPEOPERATIONSREAD / WRITE / DELETE
Sync evidence from the job that produced it
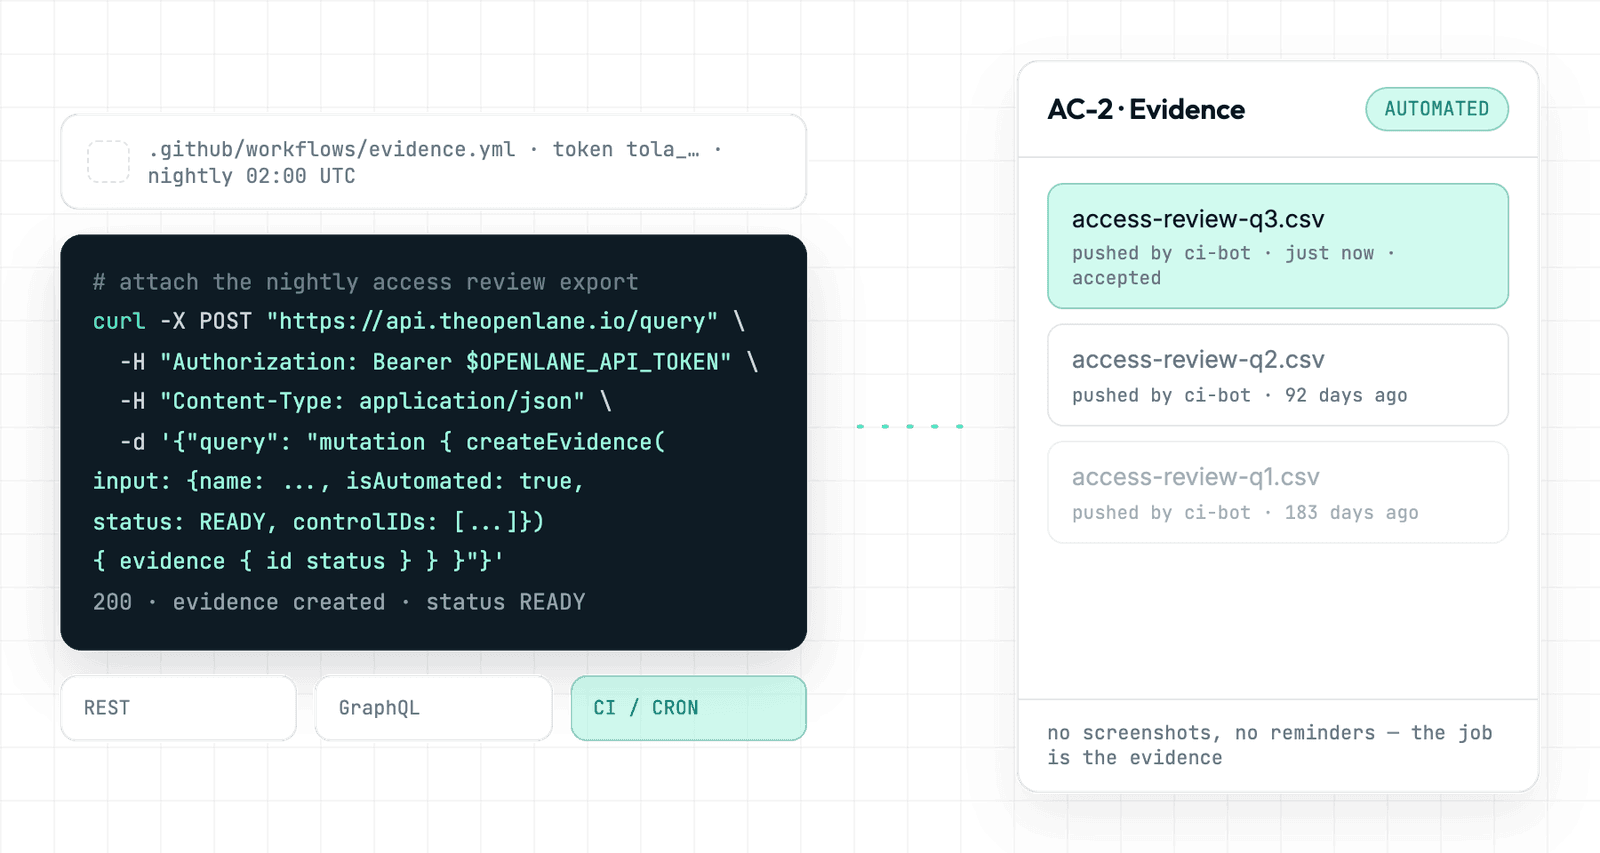
Audit prep stops being a screenshot hunt when the job that produces the proof also files it. Post evidence to the GraphQL API straight from the pipeline that generated it, whether that's a nightly access review export, a scan result, or a signed artifact, so there's nothing to capture by hand and nothing to chase before an audit.
- Post evidence over GraphQL, attached to the control it supports
- Run it on a schedule, from CI, or on demand
Controls as code, reviewed like code
Your control set gets the same review, history, and rollback as the rest of your engineering work — a change arrives through code review instead of a console click nobody logged.
- Controls and subcontrols defined in version control
- Push with the Openlane client, from CI or by hand
controls/access-control.yaml
refCode:AC-2
description:Account Management
referenceFramework:NIST 800-53
referenceFrameworkRevision:rev5
status:PREPARING
subcontrols:
- refCode:AC-2.1
description:Provisioning approvals
status:PREPARING
$ courier push controls/
✓ parsed 14 files
✓12 created · 2 updated
Controls14 SYNCED
AC-2Account Management
AC-2.1Provisioning approvals
CM-3Change control
+ 11 more from this push
git → courier → openlane · version controlled, reviewable, repeatable
Build the integration we haven't built yet
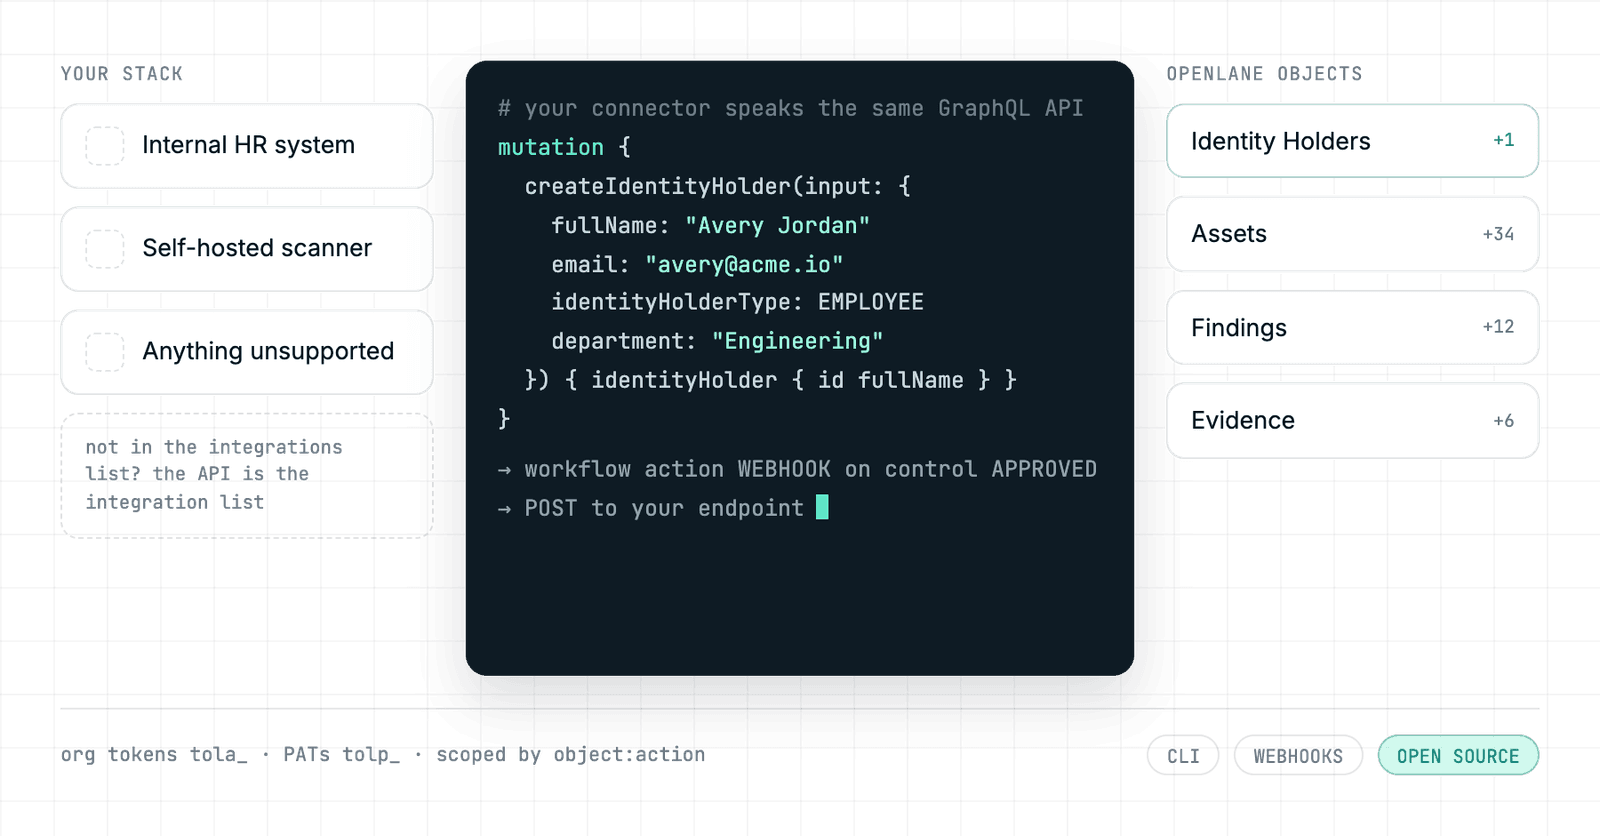
You're never blocked waiting for us to ship a connector. Every object in Openlane, from controls to evidence, is reachable over the same GraphQL API the console uses, so if your internal HR system or self-hosted scanner isn't on the integrations list, the API is the integration list.
- The same API the console runs on, with webhooks and a CLI
- Open source, so you can read exactly what it does
I wanted to build a feed of security training data from our platform into Openlane, and their APIs were easy to work with: clear documentation, straightforward authentication, and helpful examples. I was able to stand up my desired functionality very quickly, and now if a user stores an Openlane API key with us, we can reliably sync their security training data into the platform for use as evidence.
 Chad Kearney, Stronta

Built for the Terminal
An API you'd want to build on
No API upsell
The API isn't a higher tier or an add-on line item. Every plan gets the same endpoints, the same tokens, and the same webhooks.
Documented, not reverse-engineered
A published GraphQL schema and docs that describe what the console does, so you're building against a contract instead of a network tab.
Evidence from the jobs you run
Push evidence from the CI jobs you already run, and audit prep stops being a quarter-end scramble for screenshots.
Trusted By
Included with Every Plan
Build on the API the console runs on
No credit card. 30-day free trial.


'%3e%3cg id='Final-Copy-2_2_' transform='translate(1275.000000, 200.000000)'%3e%3cpath class='st0' d='M7.4,12.8h6.8l3.1-11.6H7.4C4.2,1.2,1.6,3.8,1.6,7S4.2,12.8,7.4,12.8z'/%3e%3c/g%3e%3c/g%3e%3c/g%3e%3cg id='final---dec.11-2020'%3e%3cg id='_x30_208-our-toggle' transform='translate(-1275.000000, -200.000000)'%3e%3cg id='Final-Copy-2' transform='translate(1275.000000, 200.000000)'%3e%3cpath class='st1' d='M22.6,0H7.4c-3.9,0-7,3.1-7,7s3.1,7,7,7h15.2c3.9,0,7-3.1,7-7S26.4,0,22.6,0z M1.6,7c0-3.2,2.6-5.8,5.8-5.8 h9.9l-3.1,11.6H7.4C4.2,12.8,1.6,10.2,1.6,7z'/%3e%3cpath id='x' class='st2' d='M24.6,4c0.2,0.2,0.2,0.6,0,0.8l0,0L22.5,7l2.2,2.2c0.2,0.2,0.2,0.6,0,0.8c-0.2,0.2-0.6,0.2-0.8,0 l0,0l-2.2-2.2L19.5,10c-0.2,0.2-0.6,0.2-0.8,0c-0.2-0.2-0.2-0.6,0-0.8l0,0L20.8,7l-2.2-2.2c-0.2-0.2-0.2-0.6,0-0.8 c0.2-0.2,0.6-0.2,0.8,0l0,0l2.2,2.2L23.8,4C24,3.8,24.4,3.8,24.6,4z'/%3e%3cpath id='y' class='st3' d='M12.7,4.1c0.2,0.2,0.3,0.6,0.1,0.8l0,0L8.6,9.8C8.5,9.9,8.4,10,8.3,10c-0.2,0.1-0.5,0.1-0.7-0.1l0,0 L5.4,7.7c-0.2-0.2-0.2-0.6,0-0.8c0.2-0.2,0.6-0.2,0.8,0l0,0L8,8.6l3.8-4.5C12,3.9,12.4,3.9,12.7,4.1z'/%3e%3c/g%3e%3c/g%3e%3c/g%3e%3c/g%3e%3c/svg%3e)