

Registry
System details

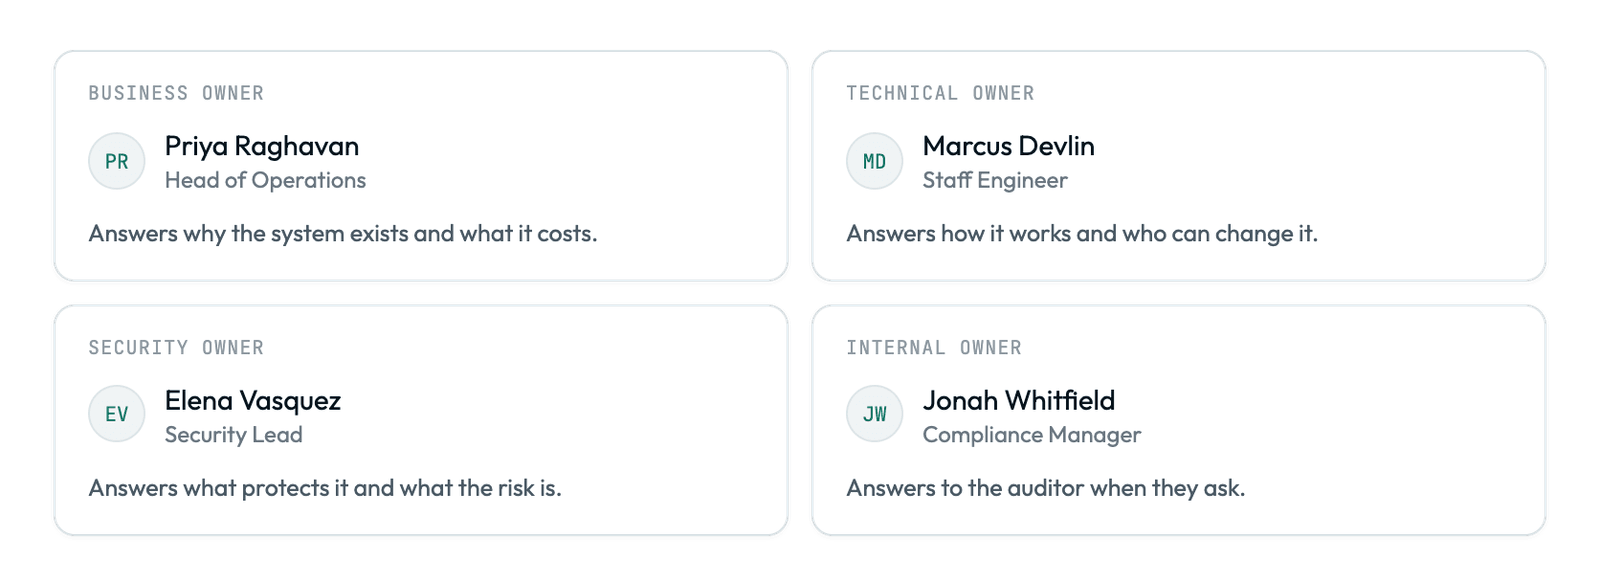
Accountability that doesn't rest on one person
No audit question lands on the wrong desk, and no system depends on one person remembering it. Ownership is recorded on the system itself, so accountability is visible before anyone has to ask.
- Ownership lives on the record, not in a wiki page
- Responsibility is distributed, not stuck on whoever set the system up
Classification that lives on the record, not in someone's head
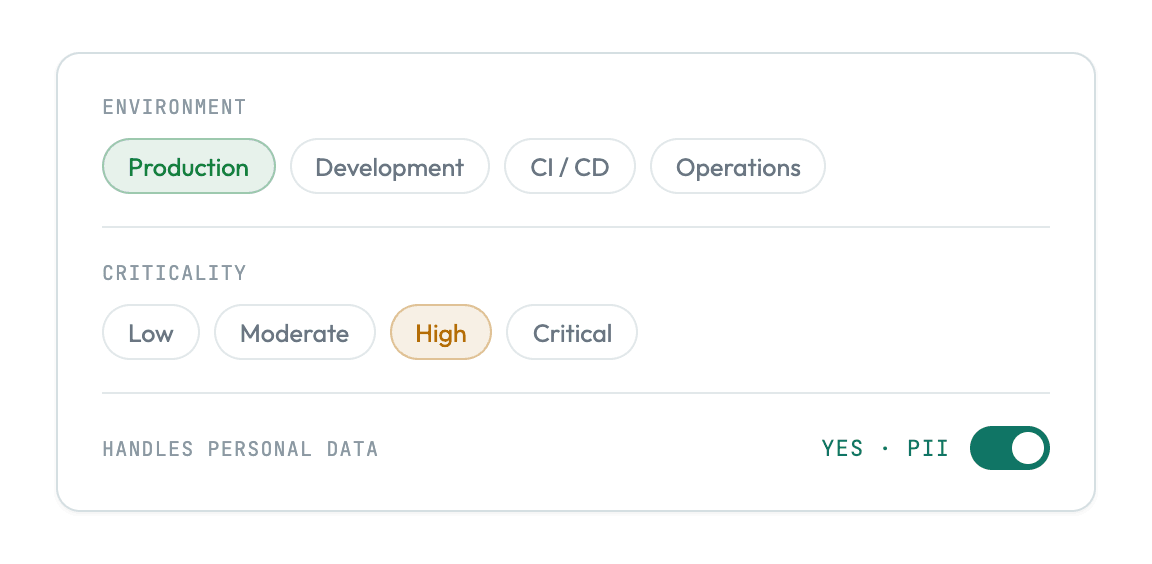
The metadata your access controls and audit scope are supposed to match lives on the record, not in someone's head. Every system carries its own classification and PII status, so scope and access decisions rest on data instead of memory.
- Classification and criticality set on every system, so nothing sits unscoped
- PII flag and region make regulated systems easy to pull for scope
Status that tells the truth
Nothing gets audited as active after it's gone. Status moves with each system's real lifecycle, so decommissioned systems stop counting as in-scope during an audit.
- Status follows each system through its lifecycle, so a record never claims a system is running after it's gone
- Decommissioning keeps the full record and history intact instead of erasing them
ActiveIn use, in scope, and reviewed on schedule.
Under reviewStill running, but something about it is being reassessed.
DeprecatedBeing wound down. Still here, so still in the record.
RetiredSwitched off, kept on file so past audits still make sense.

System Description
The metadata your audit needs
Ownership & accountability
Escalation paths and decision rights are settled on the record before an incident or an audit tests them.
Classification & PII
Every system's classification and PII status are recorded where they belong — on the record — so your access controls and audit scope match reality.
A status that holds up
Status follows each system through its lifecycle, so decommissioned systems don't get treated as in-scope during an audit.
Trusted By


'%3e%3cg id='Final-Copy-2_2_' transform='translate(1275.000000, 200.000000)'%3e%3cpath class='st0' d='M7.4,12.8h6.8l3.1-11.6H7.4C4.2,1.2,1.6,3.8,1.6,7S4.2,12.8,7.4,12.8z'/%3e%3c/g%3e%3c/g%3e%3c/g%3e%3cg id='final---dec.11-2020'%3e%3cg id='_x30_208-our-toggle' transform='translate(-1275.000000, -200.000000)'%3e%3cg id='Final-Copy-2' transform='translate(1275.000000, 200.000000)'%3e%3cpath class='st1' d='M22.6,0H7.4c-3.9,0-7,3.1-7,7s3.1,7,7,7h15.2c3.9,0,7-3.1,7-7S26.4,0,22.6,0z M1.6,7c0-3.2,2.6-5.8,5.8-5.8 h9.9l-3.1,11.6H7.4C4.2,12.8,1.6,10.2,1.6,7z'/%3e%3cpath id='x' class='st2' d='M24.6,4c0.2,0.2,0.2,0.6,0,0.8l0,0L22.5,7l2.2,2.2c0.2,0.2,0.2,0.6,0,0.8c-0.2,0.2-0.6,0.2-0.8,0 l0,0l-2.2-2.2L19.5,10c-0.2,0.2-0.6,0.2-0.8,0c-0.2-0.2-0.2-0.6,0-0.8l0,0L20.8,7l-2.2-2.2c-0.2-0.2-0.2-0.6,0-0.8 c0.2-0.2,0.6-0.2,0.8,0l0,0l2.2,2.2L23.8,4C24,3.8,24.4,3.8,24.6,4z'/%3e%3cpath id='y' class='st3' d='M12.7,4.1c0.2,0.2,0.3,0.6,0.1,0.8l0,0L8.6,9.8C8.5,9.9,8.4,10,8.3,10c-0.2,0.1-0.5,0.1-0.7-0.1l0,0 L5.4,7.7c-0.2-0.2-0.2-0.6,0-0.8c0.2-0.2,0.6-0.2,0.8,0l0,0L8,8.6l3.8-4.5C12,3.9,12.4,3.9,12.7,4.1z'/%3e%3c/g%3e%3c/g%3e%3c/g%3e%3c/g%3e%3c/svg%3e)