
Security and Compliance, Connected
Build the program behind trust.
No credit card. 30-day free trial.
 + CreateHomeComplianceRegistryTrust CenterExposureAutomationACAcme CorpOWNER
ComplianceProgramsControlsEvidencePoliciesProceduresStandards Catalog
Programs · SOC 2 Type IIKW
Evidence Submitted0%0%0 of 141141 Controls
Evidence Accepted0%0%0 of 141141 Controls
Evidence Rejected0%0%0 of 141141 Controls
Control statusGo to controls0OF 1410Created0Outstanding0Changes requested0Pending review0Completed accepted
Outstanding tasksView TasksSecurity AwarenessIn ProgressKWKelsey WatersDisaster Recovery PlanIn ProgressMAMatthew AndersonDefine 4-level data classificationIn ProgressMAMatthew Anderson
Control Environment0/14 approvedCC1.1.1DraftA Code of Conduct Policy communicates company values and behavioral standards to personnel.KWKelsey WatersCC1.1.2DraftEmployees complete an acknowledgment form upon hire indicating they have been given access to the code of conduct.KWKelsey WatersCC1.2.1DraftSenior management assigns responsibility for defining and implementing security policies to security leadership.KWKelsey Waters
Trust Center published


Where the Time Goes
Most of the effort
is not the audit


Too many tools
Controls, evidence, and policies live in separate systems, so you reconcile them by hand before every review.
Evidence Checklist
Evidence Checklist
Manual work
Evidence gets gathered again each cycle because nothing records where it came from or which control it proves.
Copying Files..._□×
Copying:
Project_Files_Archive_Final_v7.zip
Estimated time left:Transfer rate:
Fixed templates
Pre-written controls describe someone else's process. You either change how you work to match them or explain the gap at every audit.
Trusted By


The Openlane Platform
Build and operate the compliance program that fits your business
Look past the checklist
Openlane connects what you promise, how you operate it, and where the risk lies — one record you can show to customers and auditors.
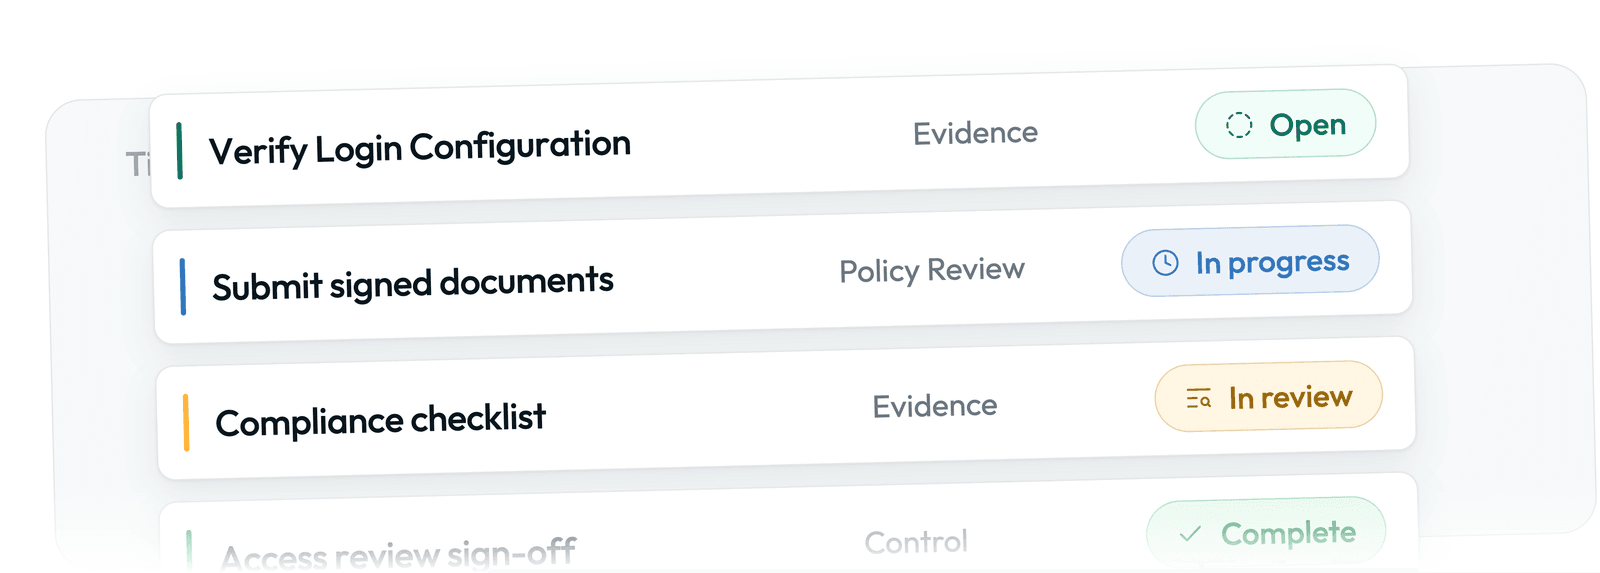
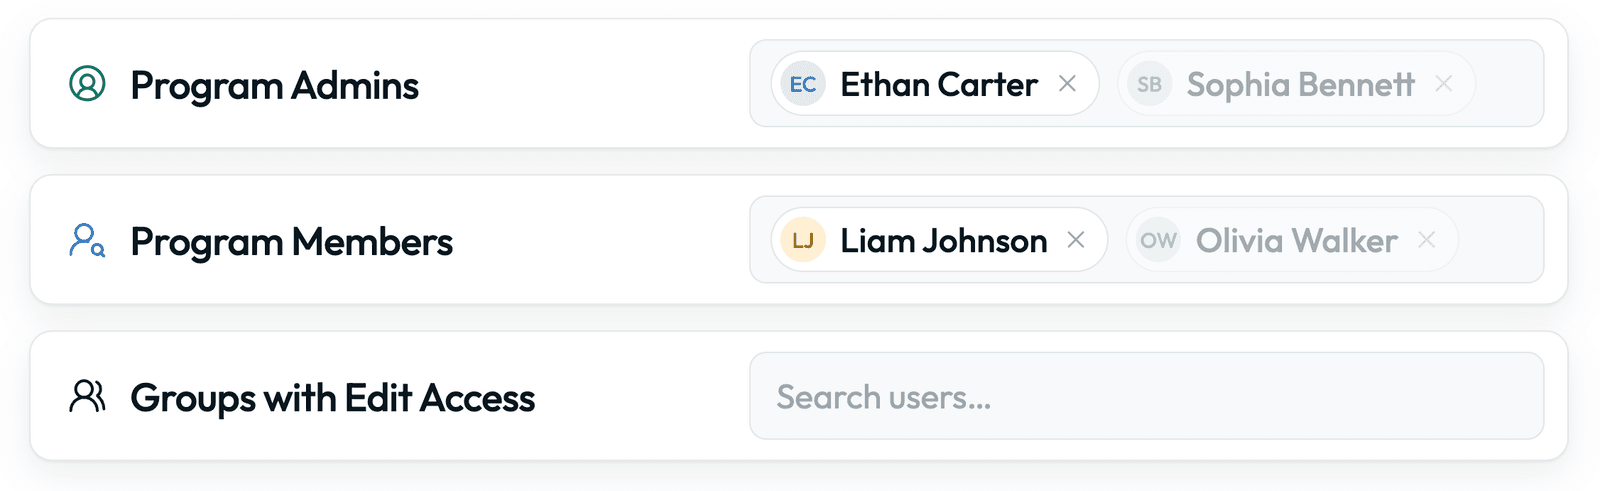
Give your security program a front door
Give prospects, customers, and auditors a controlled view of your program. Layered access and unlimited seats mean you decide who sees what.
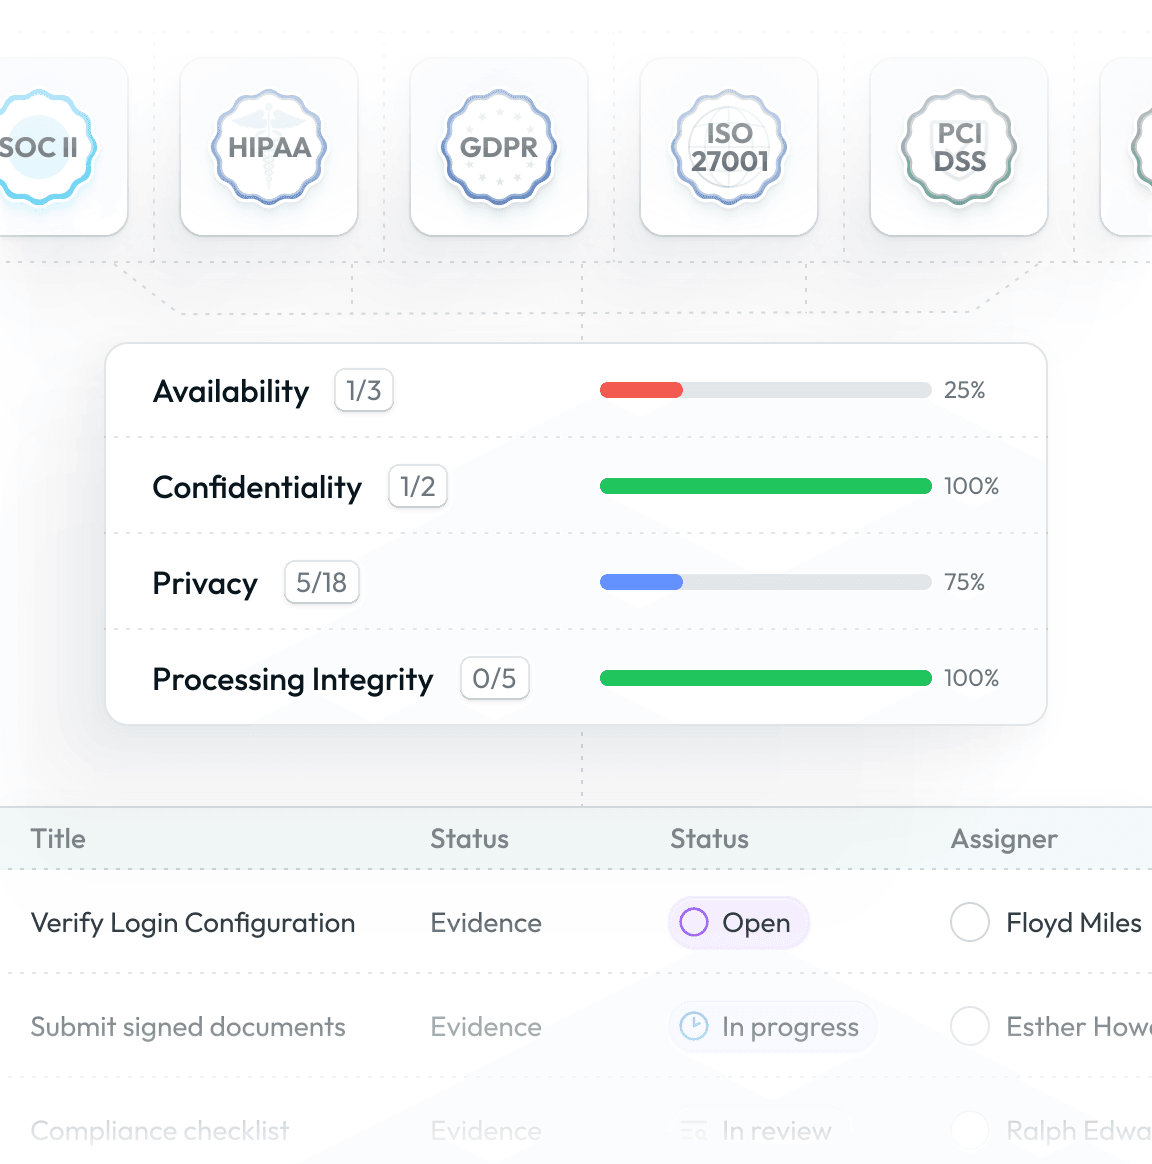
Map one program across your standards
Add unlimited frameworks and reuse controls, policies, and evidence across overlapping requirements. Coordinate at scale without losing context.
 Native Integrations
Work with the tools
you already use
 Amazon Web Services
 Authentik
 Cloudflare
 GitHub
 Google Cloud Security Command Center
 Google Drive
 Google Workspace
 Microsoft Defender for CloudMicrosoft Entra ID
 Microsoft OneDriveMicrosoft TeamsOktaSlack
 TailscaleAmazon Web ServicesAuthentikCloudflareGitHubGoogle Cloud Security Command CenterGoogle DriveGoogle WorkspaceMicrosoft Defender for CloudMicrosoft Entra IDMicrosoft OneDriveMicrosoft TeamsOktaSlackTailscale

Every other vendor made us upgrade just to enable SSO or add more users. Openlane doesn't gate essential security features behind a pricing wall — it's refreshing to work with a platform that values capability over upsell.
 Matthew Kanakidis, RentBamboo
Why Teams Choose Openlane
What changes when
the program is connected

Less manual work
Evidence, policies, and controls stay connected, so an update lands once and carries to everything it applies to.

Simpler audits
Evidence stays tied to the control it demonstrates, and a read-only Auditor role lets your auditor review it in place.

One record for every team
Unlimited users and layered permissions give each department its own view of the same program.

Security reviews answered up front
Answer enterprise security reviews from the same records your team operates, published in a Trust Center you control.

Current after the first report
Renewal dates, recurring reviews, and control history keep the program current long after the first report is signed.

One program, many standards
Map one control to SOC 2, ISO 27001, GDPR, and any other framework that shares the requirement, with no charge per standard.
The numbers teams report
82%

less time spent on evidence collection
80+
hours saved achieving compliance
12+
compliance frameworks supported
12+ compliance frameworks
across security, privacy, and AI


Go deeper on compliance
From the Blog
SOC 2: A Practical Guide
What SOC 2 involves, what auditors look for, and how growing companies get through it.
Read the GuideFrom the Blog
What is a Trust Center?
What a trust center does, what to share, and when your company needs one.
Read the GuideFrom the Blog
AI Usage Policies That Work
How to write an AI usage policy your engineering team will follow.
Read the GuideStart With the Work in Front of You
Build the program your business runs
No credit card. 30-day free trial.


'%3e%3cg id='Final-Copy-2_2_' transform='translate(1275.000000, 200.000000)'%3e%3cpath class='st0' d='M7.4,12.8h6.8l3.1-11.6H7.4C4.2,1.2,1.6,3.8,1.6,7S4.2,12.8,7.4,12.8z'/%3e%3c/g%3e%3c/g%3e%3c/g%3e%3cg id='final---dec.11-2020'%3e%3cg id='_x30_208-our-toggle' transform='translate(-1275.000000, -200.000000)'%3e%3cg id='Final-Copy-2' transform='translate(1275.000000, 200.000000)'%3e%3cpath class='st1' d='M22.6,0H7.4c-3.9,0-7,3.1-7,7s3.1,7,7,7h15.2c3.9,0,7-3.1,7-7S26.4,0,22.6,0z M1.6,7c0-3.2,2.6-5.8,5.8-5.8 h9.9l-3.1,11.6H7.4C4.2,12.8,1.6,10.2,1.6,7z'/%3e%3cpath id='x' class='st2' d='M24.6,4c0.2,0.2,0.2,0.6,0,0.8l0,0L22.5,7l2.2,2.2c0.2,0.2,0.2,0.6,0,0.8c-0.2,0.2-0.6,0.2-0.8,0 l0,0l-2.2-2.2L19.5,10c-0.2,0.2-0.6,0.2-0.8,0c-0.2-0.2-0.2-0.6,0-0.8l0,0L20.8,7l-2.2-2.2c-0.2-0.2-0.2-0.6,0-0.8 c0.2-0.2,0.6-0.2,0.8,0l0,0l2.2,2.2L23.8,4C24,3.8,24.4,3.8,24.6,4z'/%3e%3cpath id='y' class='st3' d='M12.7,4.1c0.2,0.2,0.3,0.6,0.1,0.8l0,0L8.6,9.8C8.5,9.9,8.4,10,8.3,10c-0.2,0.1-0.5,0.1-0.7-0.1l0,0 L5.4,7.7c-0.2-0.2-0.2-0.6,0-0.8c0.2-0.2,0.6-0.2,0.8,0l0,0L8,8.6l3.8-4.5C12,3.9,12.4,3.9,12.7,4.1z'/%3e%3c/g%3e%3c/g%3e%3c/g%3e%3c/g%3e%3c/svg%3e)