

Openlane vs Drata
| Feature |  |  |
|---|---|---|
| Coverage & configurability | ||
| Author your own controls | Your own control language | Supported |
| One control, every shared framework | Map once, reuse everywhere | Supported |
| Adding frameworks | Unlimited, no per-standard charge | Commonly per framework; verify with vendor |
| Extensibility & developer | ||
| API & developer surface | GraphQL API, webhooks, CLI | REST API |
| API tokens | Included; scoped by object & action | Not publicly detailed |
| Filter integration data before ingestion | Configurable expressions, pre-ingestion | Not publicly detailed |
| Platform breadth | ||
| Product areas in one platform | Five connected areas | Separate product families |
| Risk & exposure management | In the same record as controls | Vulnerability & Asset Management sub-product |
| Asset & personnel registry | Connected operating record | Asset auto-discovery; personnel from HR systems |
| Trust Center | Separate module, published price; deep brand control | SafeBase (acquired) |
| Access & deployment | ||
| Access control model | Layered, real-time (org → object) | Role-based; user access reviews run on a schedule |
| SSO, 2FA & permissions | Included on every plan | Not publicly detailed |
| Open-source core | Yes — source on GitHub | Proprietary |
| Cost & pricing | ||
| Published pricing | On the pricing page | Personalized quote |
| Per-user fees | None; unlimited users | Not publicly detailed |
Product capabilities and packaging change. This comparison reflects publicly available vendor information as of September 11, 2026. Confirm current details with each vendor.
Why teams choose Openlane over Drata

Everything an auditor or customer asks for is already connected, so at audit time you assemble nothing — the proof sits on the same record as the control that produced it. Drata packages that coverage as separate product families.
- Risk, vendor, and registry data live on that record, not in a second tool.
- Its trust center is the acquired SafeBase product, still separately branded.

Write controls in your own language instead of fitting your program to a vendor's taxonomy, then automate against the same GraphQL API the console itself runs on. Drata maps your requirements onto its proprietary Drata Control Framework and exposes a REST API.
- Map one control once and reuse it across every framework that shares the requirement.
- GraphQL API, webhooks, and a CLI — the same surface the console uses.
- Tokens scoped by object and action, so automation reaches only what it should.

Permissions match the work as it changes, layered from the whole organization down to a single object, so access reflects what people do today rather than what a quarterly review last recorded. Drata's User Access Reviews run on a schedule, one active cycle at a time.
- Exempt a member or domain from SSO while MFA stays enforced.
- Included on every plan, with unlimited users and no per-seat charge.

Know what Openlane costs before you talk to anyone — the price is on our pricing page, so you can plan a budget by reading rather than by booking a demo. Drata's price comes as a personalized quote after a sales conversation.
- Monthly or annual, both listed on our pricing page.
- Start a 30-day free trial with no credit card.
Migrate to Openlane
- No credit card required
- Full Compliance module for 30 days
- Unlimited users, no per-seat charge
- CSV and structured-file bulk import
- Pre-built control libraries
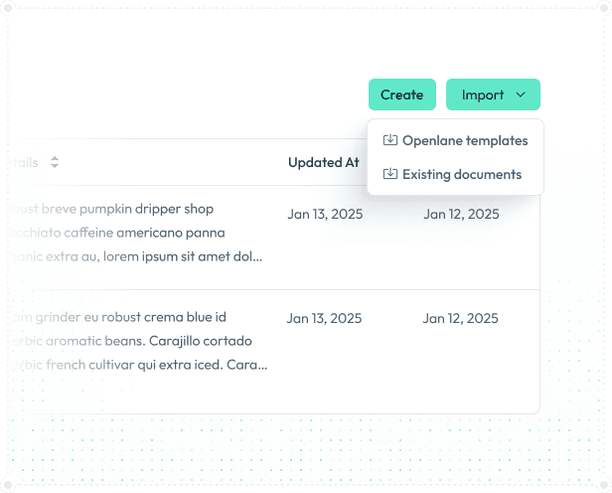
- Upload existing documents
- Use policy templates
- Define audit scope
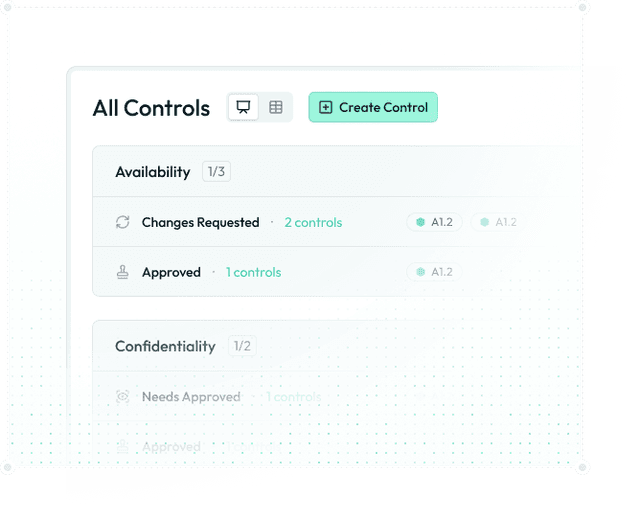
- Assign control ownership


'%3e%3cg id='Final-Copy-2_2_' transform='translate(1275.000000, 200.000000)'%3e%3cpath class='st0' d='M7.4,12.8h6.8l3.1-11.6H7.4C4.2,1.2,1.6,3.8,1.6,7S4.2,12.8,7.4,12.8z'/%3e%3c/g%3e%3c/g%3e%3c/g%3e%3cg id='final---dec.11-2020'%3e%3cg id='_x30_208-our-toggle' transform='translate(-1275.000000, -200.000000)'%3e%3cg id='Final-Copy-2' transform='translate(1275.000000, 200.000000)'%3e%3cpath class='st1' d='M22.6,0H7.4c-3.9,0-7,3.1-7,7s3.1,7,7,7h15.2c3.9,0,7-3.1,7-7S26.4,0,22.6,0z M1.6,7c0-3.2,2.6-5.8,5.8-5.8 h9.9l-3.1,11.6H7.4C4.2,12.8,1.6,10.2,1.6,7z'/%3e%3cpath id='x' class='st2' d='M24.6,4c0.2,0.2,0.2,0.6,0,0.8l0,0L22.5,7l2.2,2.2c0.2,0.2,0.2,0.6,0,0.8c-0.2,0.2-0.6,0.2-0.8,0 l0,0l-2.2-2.2L19.5,10c-0.2,0.2-0.6,0.2-0.8,0c-0.2-0.2-0.2-0.6,0-0.8l0,0L20.8,7l-2.2-2.2c-0.2-0.2-0.2-0.6,0-0.8 c0.2-0.2,0.6-0.2,0.8,0l0,0l2.2,2.2L23.8,4C24,3.8,24.4,3.8,24.6,4z'/%3e%3cpath id='y' class='st3' d='M12.7,4.1c0.2,0.2,0.3,0.6,0.1,0.8l0,0L8.6,9.8C8.5,9.9,8.4,10,8.3,10c-0.2,0.1-0.5,0.1-0.7-0.1l0,0 L5.4,7.7c-0.2-0.2-0.2-0.6,0-0.8c0.2-0.2,0.6-0.2,0.8,0l0,0L8,8.6l3.8-4.5C12,3.9,12.4,3.9,12.7,4.1z'/%3e%3c/g%3e%3c/g%3e%3c/g%3e%3c/g%3e%3c/svg%3e)